Global Race to Patch PHP Security Flaws After Critical Vulnerabilities Discovered
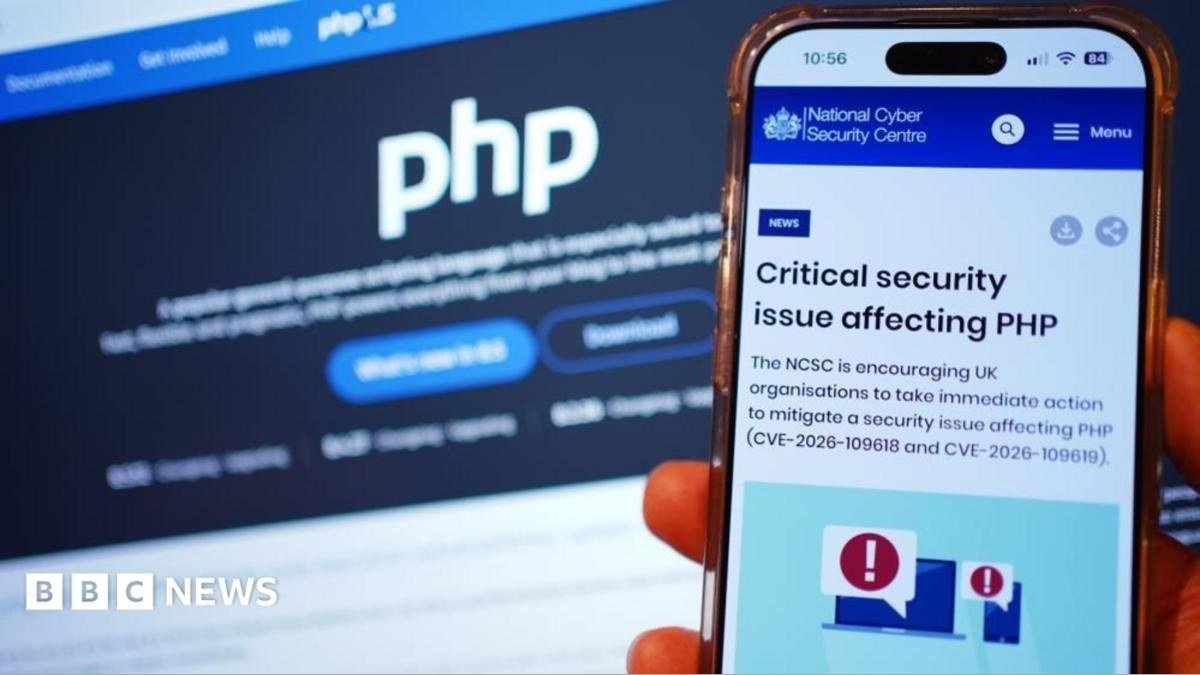
Organisations, businesses, and governments worldwide are rushing to update their computer systems following the discovery of critical vulnerabilities in PHP, a widely used back-end programming language. The security flaws, dubbed "php2shell," were inherent in the language itself and affected many past versions, putting millions of websites at potential risk.
The vulnerabilities were uncovered by cyber-security firms Wiz and Calif, partly using tools from OpenAI, after being theorised by the PHP Foundation in 2024. According to Wiz, PHP powers approximately 70% of the world's websites, including major platforms like Wikipedia, online retail stores, and content systems such as WordPress, alongside frameworks like Laravel, Symfony, and Drupal. The non-profit PHP Foundation warned that the flaw could allow unauthenticated attackers to remotely execute code on vulnerable servers under specific conditions.
Widespread Service Disruptions and Precautionary Measures
Websites across the globe were taken offline on Wednesday and Thursday as developers released patches and system administrators worked to secure their infrastructure. In the UK, 32 government services were rendered unavailable and four were partially unavailable due to precautionary protections, according to tech minister Baroness Lloyd of Effra. Downing Street confirmed that no major UK public-facing critical services were impacted.
Disruptions also affected local businesses and international entities. In South Wales, an MOT garage reported being unable to process paperwork or issue online certificates since Wednesday morning. Internationally, France's telecommunications provider Orange temporarily suspended access to certain global services while deploying fixes. Meanwhile, Finnish government sites, a Dutch cyber-security agency, and parts of Wikipedia returned to normal operations by Thursday after brief downtime.
Exploitation Attempts Surge Rapidly
While no successful breaches or attacks have been reported, internet infrastructure companies reported a massive surge in exploitation attempts. Cloudflare chief executive Matthew Prince stated that the firm detected thousands of exploitation attempts in the 10 hours prior to the public announcement, which escalated to millions within hours following the release. Amazon also detected exploitation attempts but maintained normal website operations.
Olly Whitehouse, chief technology officer at the National Cyber Security Centre (NCSC), described the event as "unprecedented" and noted that its impact would be felt universally, though there were no indications of successful hacker breaches. Cyber-security experts warned that while attackers now attempt to exploit vulnerabilities within hours or days rather than weeks, the full impact of the flaw could take months to become entirely clear.
0 YORUMLAR
Bu KONUYA henüz yorum yapılmamış. İlk yorumu sen yaz...